| SYSTEM INFORMATION | |
|---|---|
| OS type and version | Debian 12 |
| Webmin version | 2.653 |
| Virtualmin version | 8.1.0 GPL |
On my old Debian 11 server fail2ban used ipsets.
/etc/fail2ban/jail.d/–000-firewalld.conf
# This file created by Virtualmin to enable firewalld-cmd actions by
# default. It can be removed, if you use a different firewall.
[DEFAULT]
banaction = firewallcmd-ipset[actiontype="<multiport>"]
banaction_allports = firewallcmd-ipset[actiontype="<allports>"]
On Debian 13 with a clean install I have this:
/etc/fail2ban/jail.d/virtualmin-firewalld.conf
# This file was created by the Virtualmin installer to enable the use of
# Firewalld rich rules with Fail2ban
[DEFAULT]
banaction = firewallcmd-rich-rules
banaction_allports = firewallcmd-rich-rules
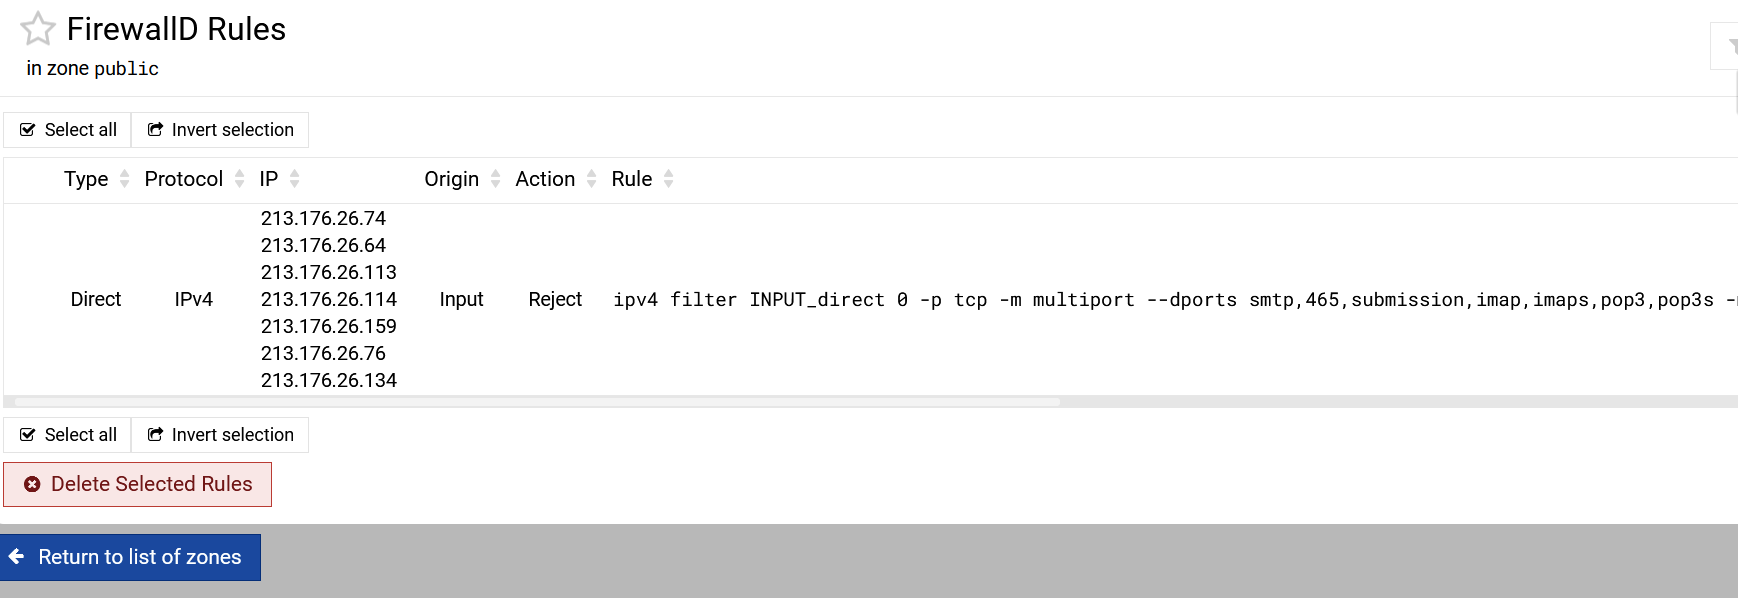
Which seems to have a problem discussed here.
But my question is: Aren’t ipset much more efficient, faster and cleaner?
Can I just change this config to ipsets to use that? The default install has ipset installed