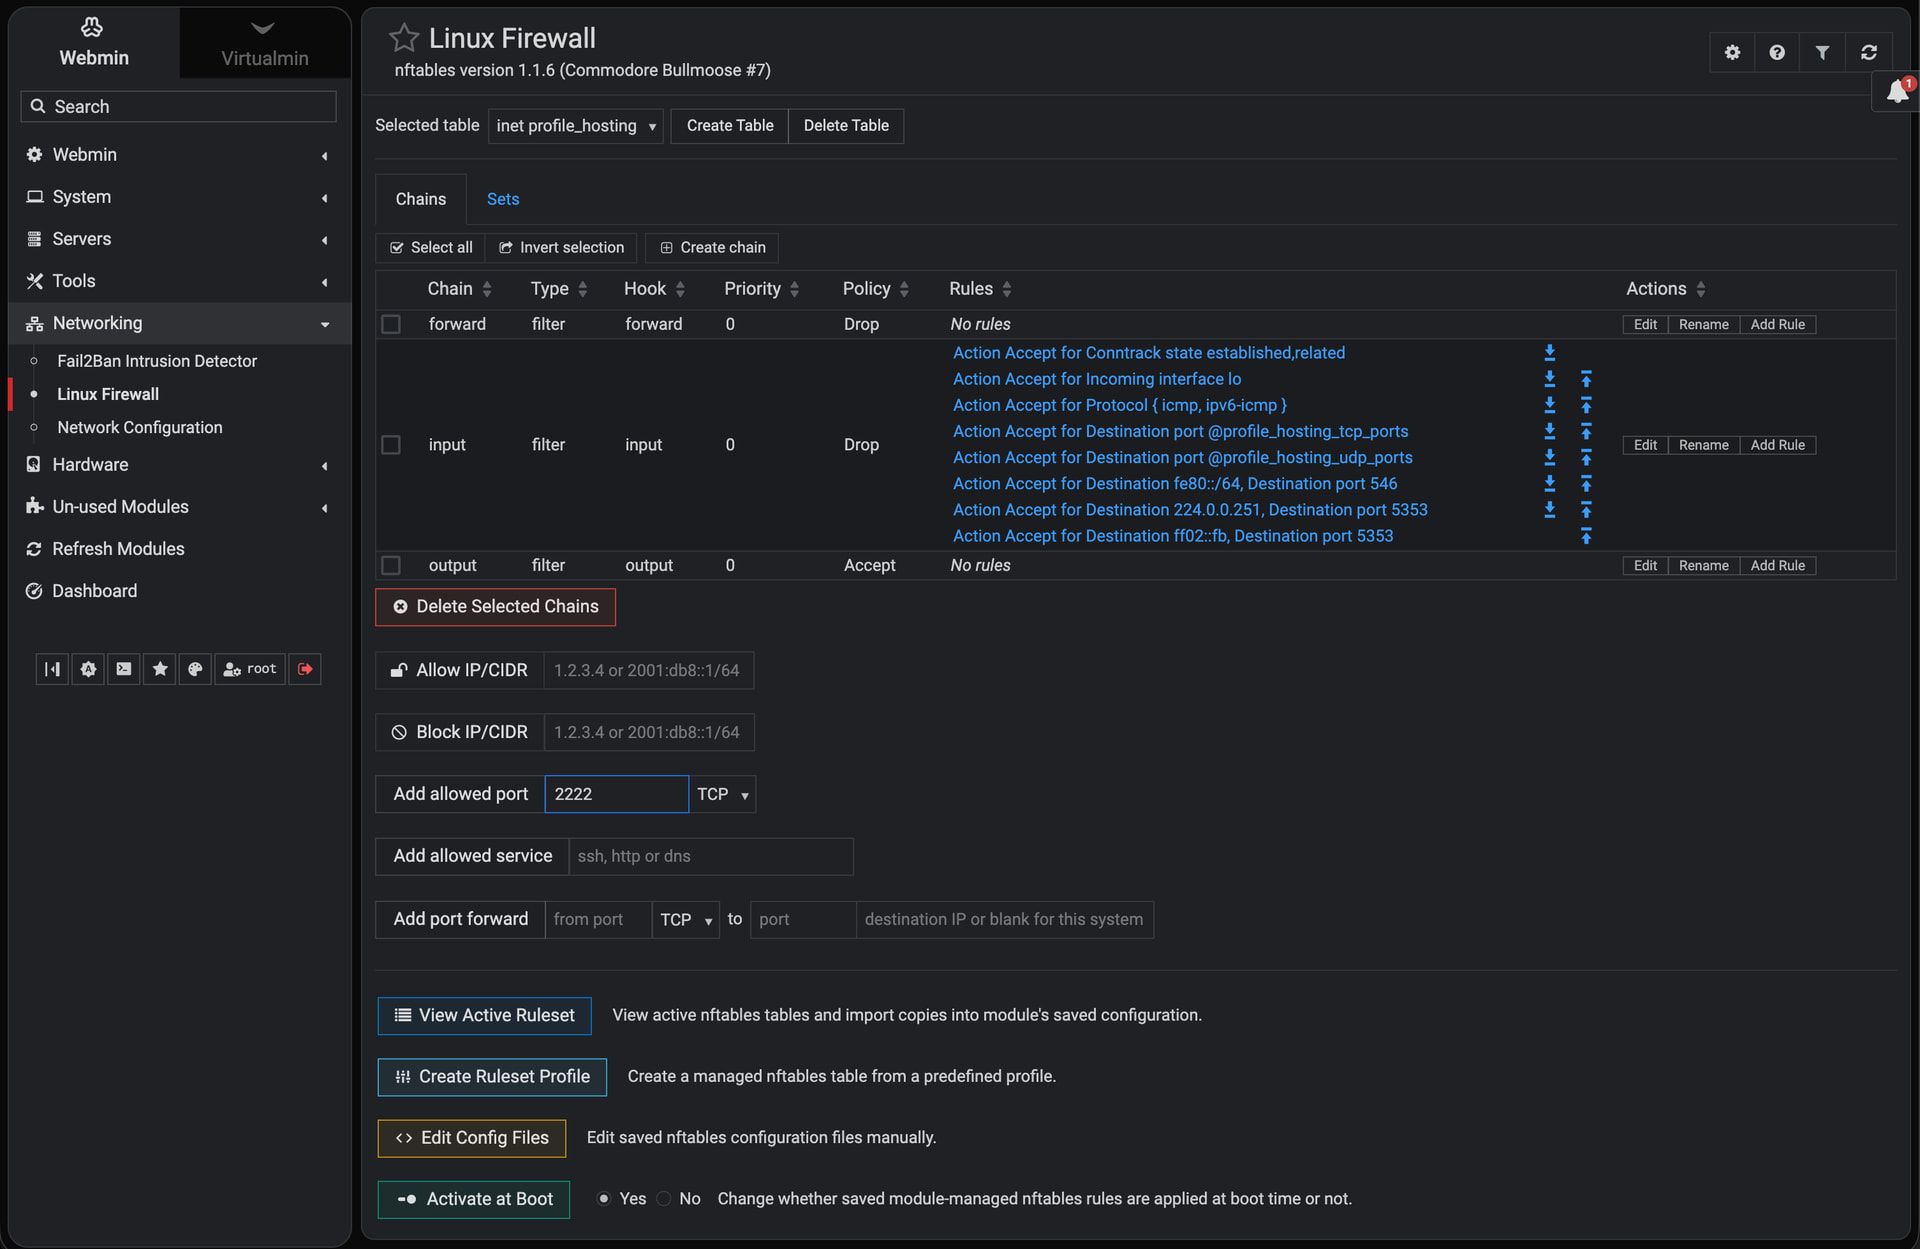
Before switching a few VMin servers from firewalld to the new nftables module I have setup the nftables module with webmin at a fresh installed debian server on bare metal.
To get the ‘internet firewall’ module active, I needed the nft utility, a simple ‘apt-get install nftables’ did the job. The predefined ‘inet profile_hosting’ rules of the new module made the basic setup easy.
As a cli addict I looked at /etc/nftables.conf to see how I could add my favorite non-standard ssh port. No real setup there, just an empty ruleset. The real nftables setup happens to be in /etc/webmin/nftables/rules.conf, not in the standard location.
Why is the standard location not used?
After I inserted the not-standard ssh port with the webmin module I tried to find a button for a reload of the firewall rules. Could not find that, there was no automatic reload, the extra port was still blocked.
A simple ‘systemctl restart nftables’ did the job. EDIT: this was not correct, all ports were open now.
Can we have a reload button? Or did I miss something and should a reload not be needed.
@Ilia, that page looked promising to me, however I missed a button to close port 22 and made the changes with the edit button on the Sets tab. More details below after some extra tests.
I did the following:
Open the Sets tab, click the Edit Sets button for tcp ports, remove 22 and add a new nnnn port.
After that was done, the new situation was not active. Port nnnn still closed and port 22 open.
To activate the new rules I tried the usual ‘systemctl restart nftables’. This switched off the firewall, all ports were open now.
What happens is that after a reboot the settings settings stored in /etc/webmin/nftables are active, and that after a systemctl restart, the settings in /etc/nftables.conf are active. For a firewall this is a bit a dangerous combination.
Agh. It’s a bug introduced by Copilot Code Review having terrible judgment and I missed that it was introducing a bug and then every LLM since that looked at it has further entrenched it as policy rather than a bug and has introduced new layers of stupid on top of the bug. Dang. LLMs are so stupid and I’m stupid for trusting them.
I’m rolling back the behavior and simplifying things so that we’re directly editing the system nftables rules.
It started out as a very simple bug, and subsequently became quite a complicated and multilayered bug because the LLMs decided that bug was an intentional policy choice.
It was quite a lot of silly to unwind, but it also resolves a couple of other problematic behaviors and handles include files better, so it was good I spent some time with it.
In my test setup I already disabled webmin-nftables and enabled nftables at boot time. Added a set of rules to nftables.conf, and renamed all files in the webmin/nftables directory. That setup works fine and is for me simple to maintain. This survived changing rules, restarts and booting without any problem.