Question, how are the ownership/permissions set on the .hosts files in bind ?
To expand, does the VM installation script set permission defaults for these files or does VM just use the defaults that say Debian/Bind use ?
The reason for the question, as I previously mentioned we just moved 2 NS servers over to Deb 13 and have had some strange issues with .hosts file not transferring/not populating.
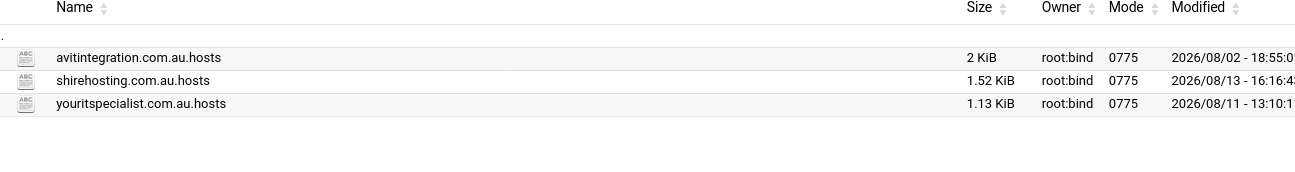
This is the permissions set on a fresh install for the .hosts files
You will see its set as root:bind, But on an older install the permissions was set to bind:bind ( everything I read also said it should be bind:bind)
What was now happening is the .host file is transferred to the NS servers blank (empty) and no matter what I did would not populate. The only way to fix this was to manually change the permissions/ownership to bind:bind which was the way the old servers were. Then the .host files populated as expected.
So to recap we have 3 x NS servers 2 we updated to Deb 13 fresh install, both have the same issue, the old one we did not touch (Deb 11) works as expected.
The Webmin “BIND DNS Server” module and its library have a function named set_ownership that handles this depending on the configuration. If file_owner is set in the module config, it uses that, otherwise, it mirrors the parent directory’s owner and group.
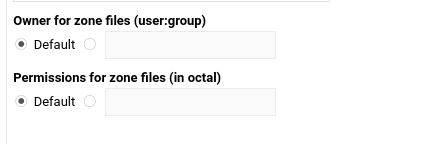
You can configure this in “Servers ⇾ BIND DNS Server ⇾ Module Config: Zone file options” using the “Owner for zone files (user:group)” option.
Sorry for the delay! I finally dug into this and reproduced it on Debian 13 and Ubuntu 24.04, and learned a Linux permissions detail I had never realized before!!
The zone transfer actually succeeds, but BIND then fails to set the file’s modification time to a specific value, because the file belongs to root.
What surprised me is that group write permission lets plain touch set the timestamps to now, but assigning an explicit date requires file ownership or CAP_FOWNER. I honestly didn’t know that!
Because BIND uses an explicit timestamp to track zone expiry, a failure in that operation also prevented it from being written to the disk, leaving behind the empty .hosts file created by Webmin, even though the transferred records are already in memory.
So, setting ownership to bind:bind fixes it. @Jamie, I’ve updated the Debian and Ubuntu default configs accordingly.
@Shirehosting, for existing installations, set Owner for zone files to bind:bind in the BIND module config, then manually change the ownership of the affected files to bind:bind as well.
Yeah, it does it internally. Yet also it can be reproduced in a normal workflow, like running touch filename works when the file has group write permission, even if it is owned by, say, root. But if you try to set a specific date with touch -d '2000-01-01' filename, it fails with a permission error.
I had already set the owners to bind:bind, but was more interested to find out why it wasn’t working, because remembering to set it at 3am in a rush is never good.