Welcome the new Virtualmin Podman Plugin

I have successfully updated to the latest podman module build and checked the config for the restart on boot option which is set to ‘always’ and I restarted the VPS and the containers show as ‘running’ but they are not.

These recipes were created in module 1.3.xx so I suspect I need to recreate / reinstall and wonder what the correct process is?

I would also like to keep the data uploaded to the container which from what I can see is possible.

Also am wanting to change the sub server for one of the containers to a different domain. Is this possible? I expect all of this is achievable but wanted some clarification before I pull the trigger and mess it up with :joy:

Containers shouldn’t need to be recreated across module versions. That sounds like a bug.

Containers created with an earlier module version should not never need reinstalling. I’d check the runtime status and let us know which recipes are affected in particular.

Hi, thanks for the reply. I have x2 recipies setup (Navidrome & Audiobookshelf) on separate sub-servers. They are working fine. I see the Podman module setting is set to ‘Start containers after reboot’ and the containers are 'rootless '.

When I reboot the VPS, the behaviour I see is that the x2 containers show as running. However, when I try to access the actual domain, I get a 503 error. Happy to supply logs or troubleshoot.

As an aside an app that looks very promising for addition to the recipes is https://bookorbit.app

Dear Ilia,

Tested rootless as suggested, confirmed UID 0 inside the container. sudo issue is gone, WireGuard interface creation now succeeds. But it now fails one step later, on iptables NAT setup:

iptables v1.8.13 (legacy): can't initialize iptables table `nat': Permission denied (you must be root)

So it looks like rootful gives real root but maps to the domain UID inside the container (breaking anything checking for UID 0), while rootless gives UID 0 inside the container but not real kernel-level netfilter access (breaking NAT). Neither mode alone satisfies both conditions that a NAT-based VPN needs.

Not expecting a quick fix here, this seems like a fundamental interaction between the two isolation models and iptables/netfilter, not a bug per se. Just closing the loop on this specific case: I’ll keep wg-easy on Docker for now, and will try the other imports (Vaultwarden, Jitsi) that don’t need NAT expecting those to work cleanly in rootless.

Thanks for all the help tracking this down, learned a lot about the plugin’s internals along the way.

It may take some time to bring things up after the reboot. When you checked, did it not work for a prolonged period after the reboot, or did you only check right after the reboot?

Thanks! Agreed! Just added it.

Yeah, it looks like wg-easy simply isn’t a good fit for a container tied to a Virtualmin virtual server cause it needs host-level networking access that conflicts with the isolation we’re trying to preserve.

Yet it may make more sense to support it through a separate, root-only Webmin module instead.

2 Likes

Huh? Can you please clarify this?

What I meant was that upgrading Virtualmin Podman doesn’t require reinstalling the containers themselves.

Great to see this live!

This would be a very handy addition:

Awesome to see this plugin live now! I’m in the process of leaving Dockhand and moving everything over. Did a reboot and found that “unless-stopped” doesn’t reboot the containers. I tried changing a couple of containers to Always and get this error:

Saving container chat ..
.. failed : error: unknown flag: --restart
See ‘podman update --help’

Saving container uptime-kuma ..
.. failed : error: unknown flag: --restart
See ‘podman update --help’

UPDATE: Looks like this may be a version problem;
podman version 4.3.1 installed. This is the latest version for Debian Bookworm. Looks like I will be upgrading to Trixie.

This looks exciting… but why?

What is the difference between these recipes and existing web apps?

They are containerised.

Thanks for the link.

OK, I think I understand what pods are a bit more, but still do not understand the pro’s/con’s of one over the other.

Containers provide a bit more isolation between applications and users, which provides some security benefits.

It is one approach to the “it works on my machine” problem. With a container, the app developer ships their exact environment (versions of the language and library dependencies, etc. exactly as tested by the dev). If the app developer ships a high-quality container, the likelihood of something going wrong with your installation of that app will be lower, because the system it runs in is not changing; the dev ships their system, and that’s what the app uses.

It reduces our workload when supporting a new application. A recipe is generally much smaller than an app installer, because we’re not solving the dependency problems. We’re just grabbing the developer’s container(s) and proxying to them. There’s a reason Ilia has been able to add support for well over 100 applications, when it took us a much longer time to get to 100 app installers. And, they will likely not corrode as rapidly. When the upstream makes changes that effect deployment, it’s probably something in the container they ship, and not something our stack needs to address. A container is a black box, where we only care about the inputs and outputs. A web app installer has to care what’s in the box. The complexity is still there, we’re just not the ones handling it.

The cons of containers: Much heavier. A container deployment will consume an order of magnitude more disk space, take longer to install, and will run its own versions of everything with much less resource sharing. While a hundred PHP applications running under PHP-FPM will share huge swaths of memory across all of them (assuming all of them are on the same versions of everything, including PHP version), a hundred containerized installations of PHP apps will share quite a lot less.

With Linux page sharing, it won’t be the “no sharing” that seems intuitively what has to happen with isolated containers, it still shares less, maybe even close to zero, depending on how many identical pages there are. It’s definitely less than in a non-containerized deployment. Every containerized app may use a different PHP and library version (what’s in the black box, you can’t readily control), and if so, the amount of sharing across those apps may be close to zero. In the usual case for non-containerized apps, you’ll have one PHP version and roughly the same libs across all your apps, lots of opportunities for shared memory. This also effects performance. There’s more CPU cache hits when everybody is using the same pages in memory.

And, you may not be able to tell very easily how much difference there is between a container deployment and a regular app running under PHP-FPM (or a Python app server or Nodejs or whatever). The memory usage you see in top and the process list module in Webmin doesn’t make it easy to tell what’s shared. 50 PHP-FPM processes will mostly be shared memory, but will look like 50 processes consuming 20MB each RES (and much more VIRT); you paid the full price for the first app running under PHP-FPM, and now each extra one using the same version and libs will consume far less, even if the app is a different one. 50 containerized apps will look like all of their component parts running in their own namespaces (database, app server, the language interpreter, maybe redis, etc.). Maybe none of it is shared with other users processes, maybe some of it is (50 identical app containers running the same app will still be able to share a bunch of memory…but 50 different PHP apps probably won’t).

1 Like

Wow, that really has helped - thanks.

Assuming you have a server with reasonable resources, is there an argument for running domains/servers via this method, rather than as a traditional web install.l, e.g. Wordpress.

Are there any performance improvements etc?

There are almost certainly performance costs for containerized apps. More memory usage means lower cache hits.

The benefits are maybe security and maybe reliability (assuming the maintainers of the container are conscientious about not breaking backward compatibility) and a wider selection of available apps.

Adding that wouldn’t be trivial, though it is possible. And, Supabase recommends at least 4 GB of RAM, 2 CPU cores, and 40 GB of storage, with 8 GB of RAM preferred—that’s quite demanding!

Thanks! That was indeed the bug in Virtualmin Podman 1.6.0, which will be fixed in the upcoming 1.7.0 release.

where do I update the containers? in portainer there is a notification icon whenever a new image can be pulled and then you can recreate the container with the same settings but as an update.

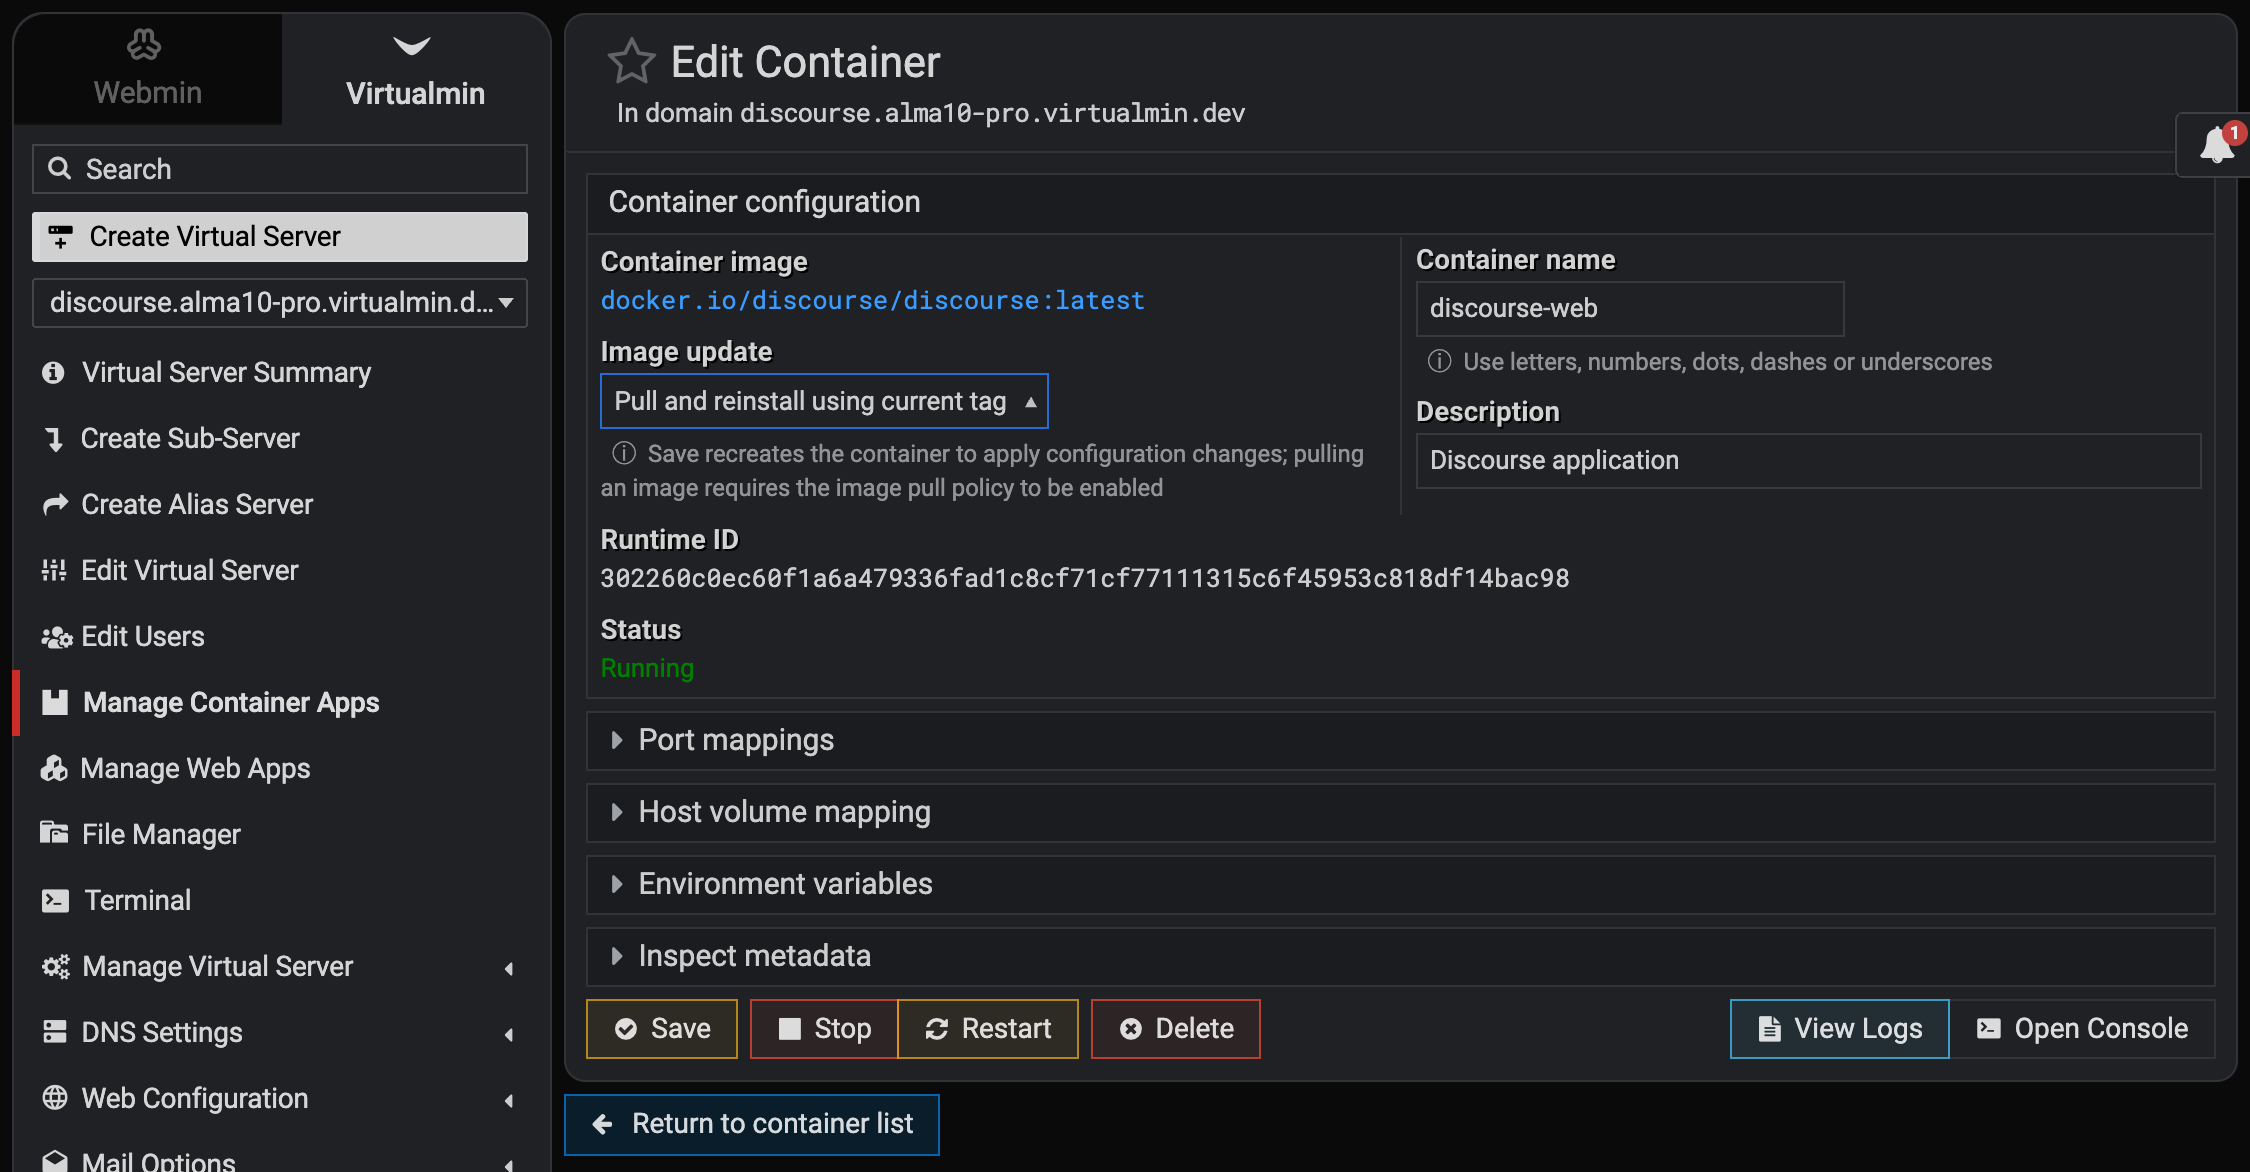
We don’t have notifications for this yet. However, you can update it by reinstalling it here:

1 Like