I have a multi-domain webserver using Virtualmin (mostly for Wordpress sites). A single (thankfully trusted) user asked for SFTP access which I granted with an approved IP through FirewallD.
He has reported, and I have confirmed, that if I WinSCP in as this user, though I land in my home directory, I can navigate out of that and at least download things like /etc/passwd (I haven’t tried deleting anything like that but that seems likely from what I am seeing).
How do I lock this user to their own home directory in this case?
Of course a user can’t delete anything. Linux is a multi-user system by design. Virtualmin works with the standard UNIX user permissions, by default. Your users can look at non-sensitive stuff (/etc/passwd has no secrets), but can’t cause any harm.
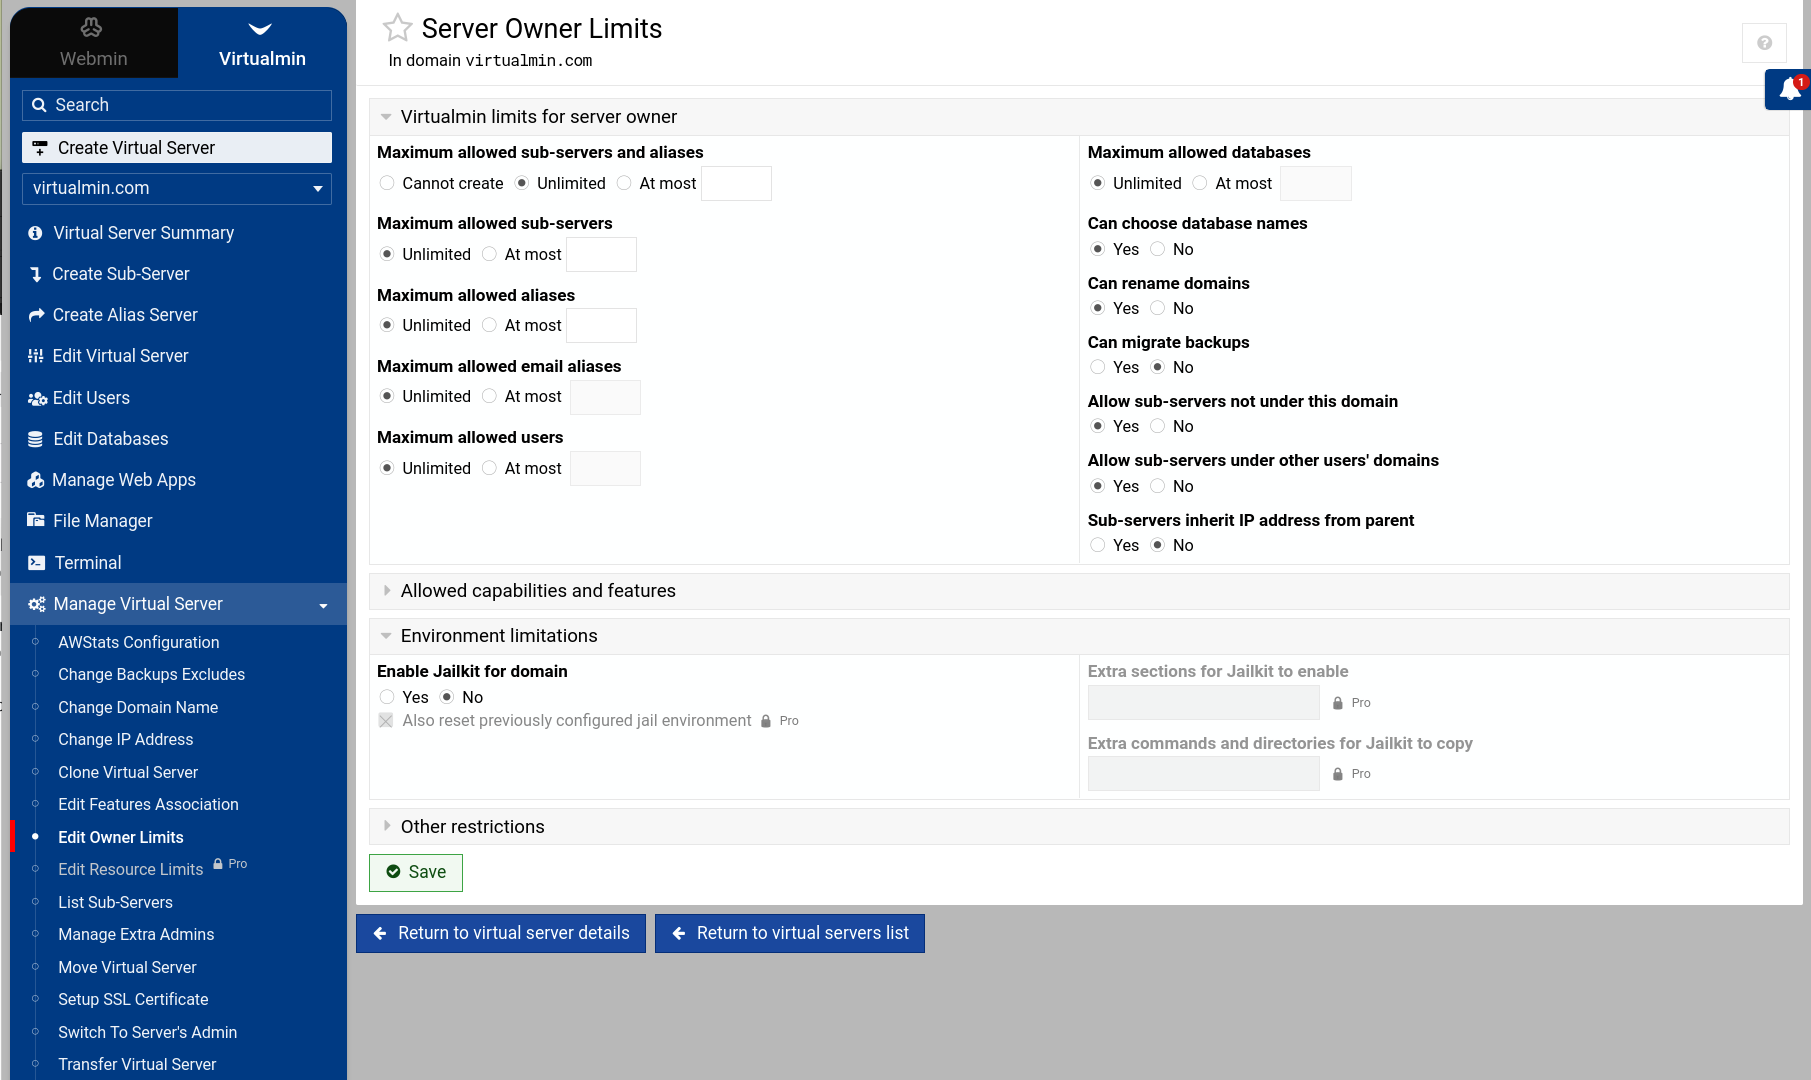
But, Virtualmin also supports jailkit for chrooting ssh users into their home.
But, you should be aware of the limitations of a jailed user (they can only run what you grant them permission to run…we have some template jails which include the basics, but you’ll almost certainly want to think about what kinds of things you want users to be able to do and add things to the jail you give them. Virtualmin currently uses Jailkit for this, so it’s worth reading up: Jailkit - chroot jail utilities
Note that Virtualmin 9 (no promises about when this is coming) is getting an overhaul in this area, to offer a Bubblewrap feature. It will likely be enabled by default, as bubblewrap can be much less disruptive than a chroot jail, and it is also actually based on security features (chroot is not a security tool, it is only accidentally shaped like one for some use cases). Because bubblewrap can be safer and can allow most functionality without jumping through hoops, we feel better about enabling it by default.