I have different domains with different contents, and some users have been created for each domain, or at least the default user. I need to upload files to the respective virtual servers, using the credentials of the default user. I do that using a script which runs rsync. Basically, this works fine, but due to the complexity of the password, I always have to look it up, which takes time. Hence I would like to switch to SSH key based login. However, I am not sure how to do that considering that I use one PC as client and have multiple users at the server side. I thought there is an option in virtualmin to create ssh keys, but I don’t find it. Was I mistaken? If so, I would appreciate a short description on how to go about it manually, and if an option exists to do it within Virtualmin, I would appreciate a pointer to the particular function.
I have become aware that I can set the basic behaviour of Virtualmin regarding SSH keys from within Webmin, but that wasn’t set to create keys by default. Once it is set, there is still the question on where to put private keys and the public keys.
I find Vultr docs pretty easy to follow on how to make the keys
I use the puttyGen method in the docs as I use putty to ssh on.
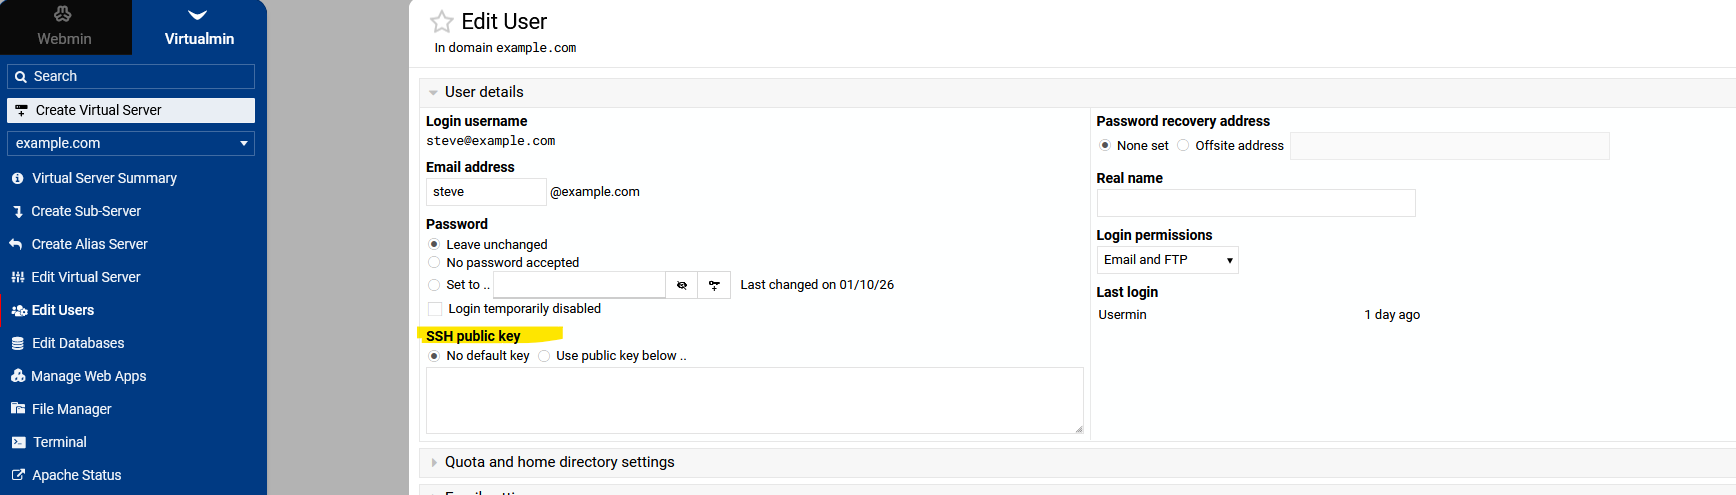
Where to put the keys question, the software you use like putty in my case has the private key, and the server holds the public key. In virtualmin there is a form input for that where you edit the user.
Virtualmin as far as I know doesn’t have a generator to create keys but the linux machine does with OpenSSH, see the vultr docs.
Thank you, @stefan1959. That helped. The Vultr docs alone weren’t enough, your additional info about Virtualmin’s features in this regard was good. Just one thing: I found the form to add the public key only in the Webmin users interface (System/Users and groups). In Virtualmin I went to the page “Edit Users” within the Virtual Server, but there I didn’t find any form to add the public key.
Anyway, after I created and added it, I tried a login and it worked perfectly.
All of your domain owner users can have the same ssh public key(s) in their authorize_keys; the file that’s checked depends on the username you’re logging in as. So, when you ssh virtualmin@virtualmin.com ssh checks /home/virtualmin/.ssh/authorized_keys for your public key…if it’s there and you have the private key, it lets you in as that user.
That wouldn’t be safe. The key pair has to be generated on your own machine, and the private key should never leave that system. Only public keys go on your servers.
But, there is a form for uploading a public key for the domain which puts it in authorized_keys for that user.
Actually not. I have two users for the domain, one is marked as owner, the other is an user I added separately. The “owner”, for whom I wanted to add a ssh key, doesn’t have that window. It only shows email options, login permissions and last login.
The other has indeed the form to add a ssh key.
Ah, that’s why. I didn’t know that. So basically I just copy the public key into the owner’s .ssh/authorized_keys file? Can it cause problems if I add an individual key for that user?