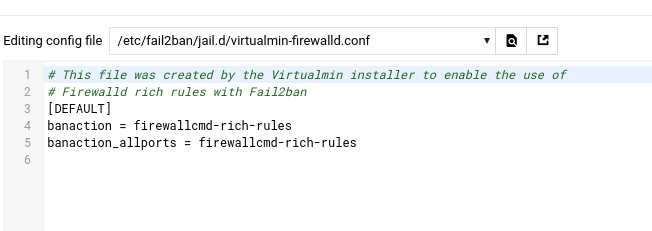
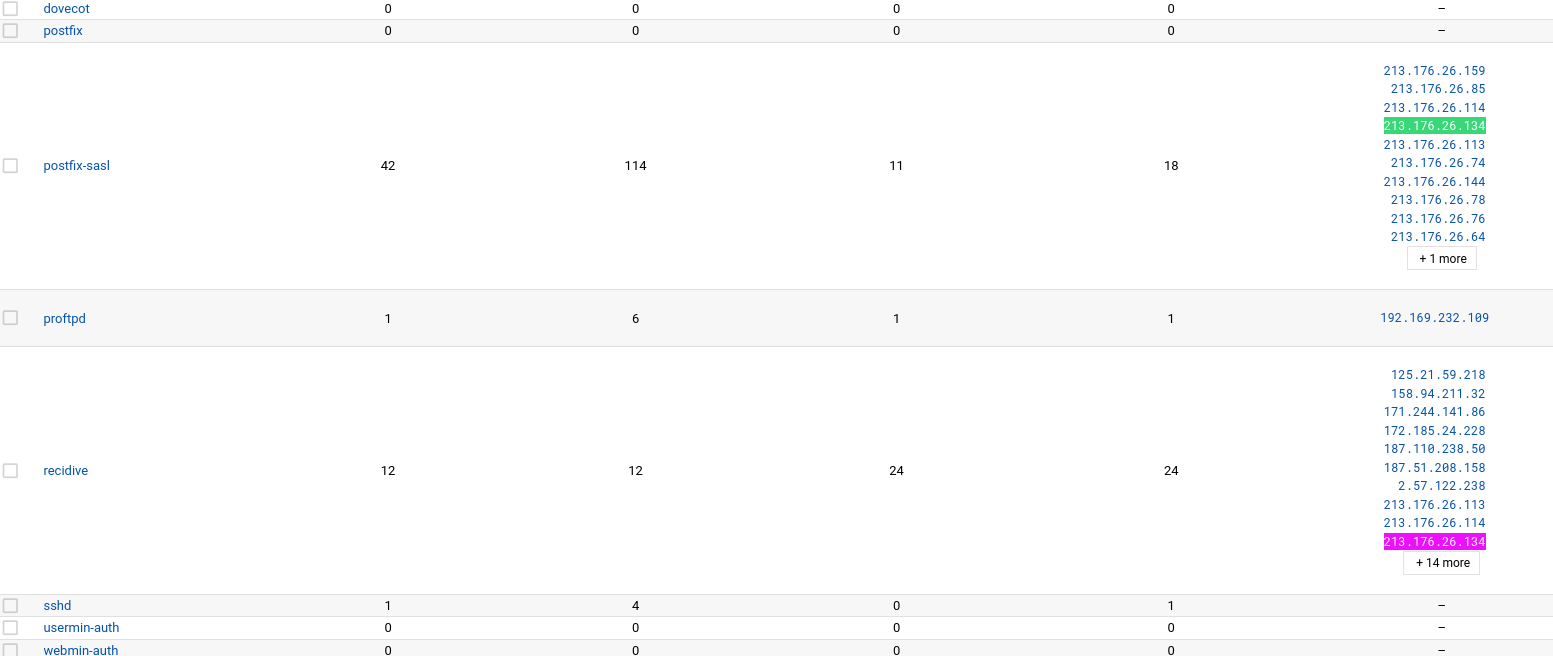
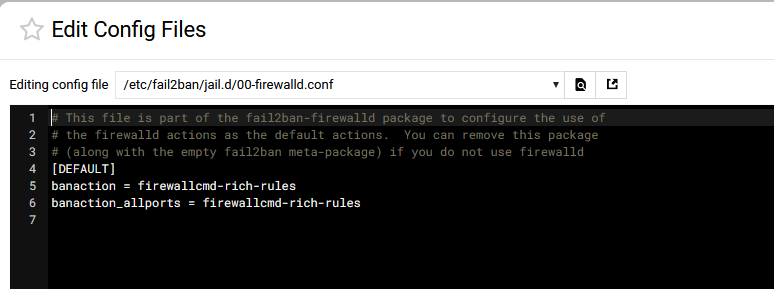
We have just moved our 2 NS servers over to Deb 13 and I have noticed that there now appears to be a new virtualmin config file that is created at installation time for F2B
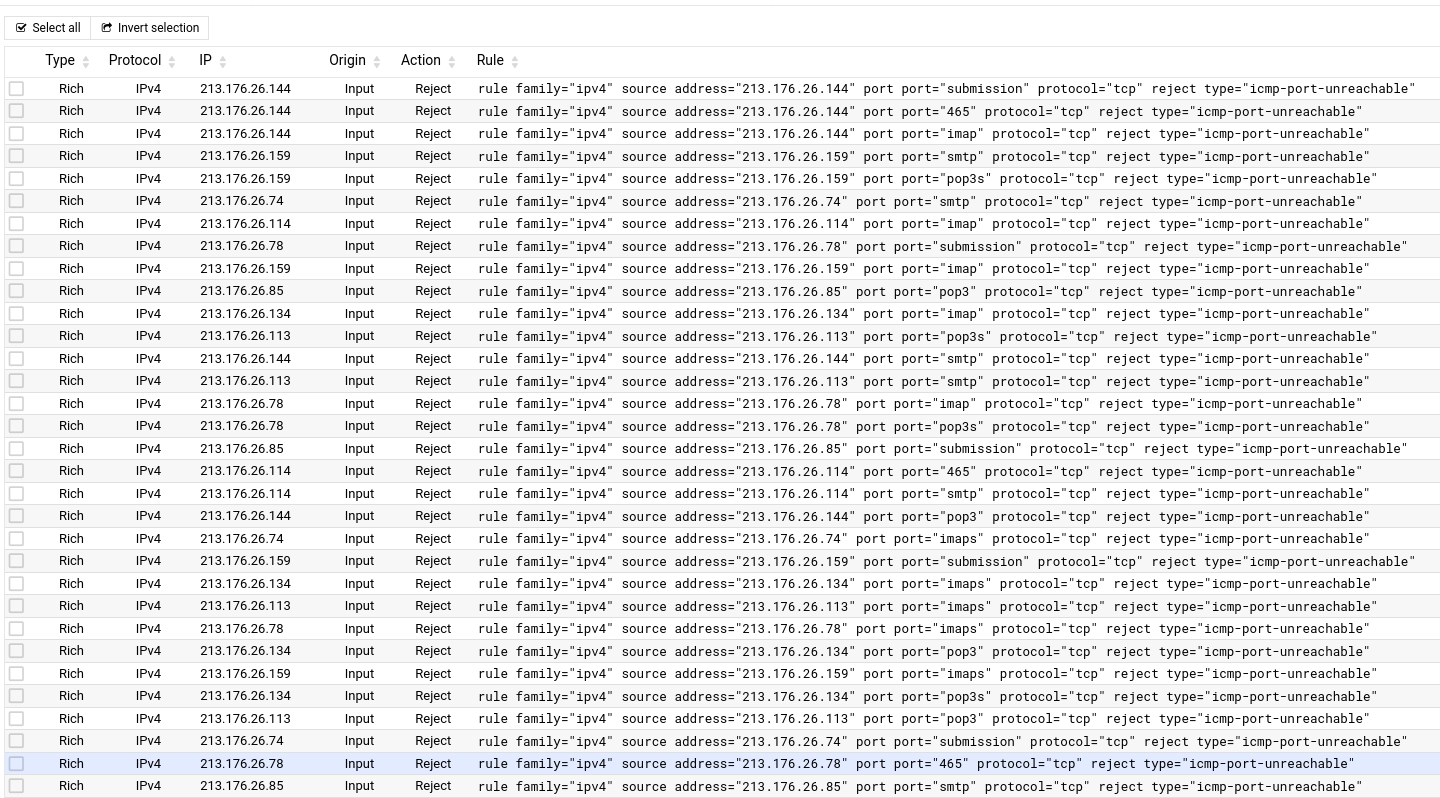
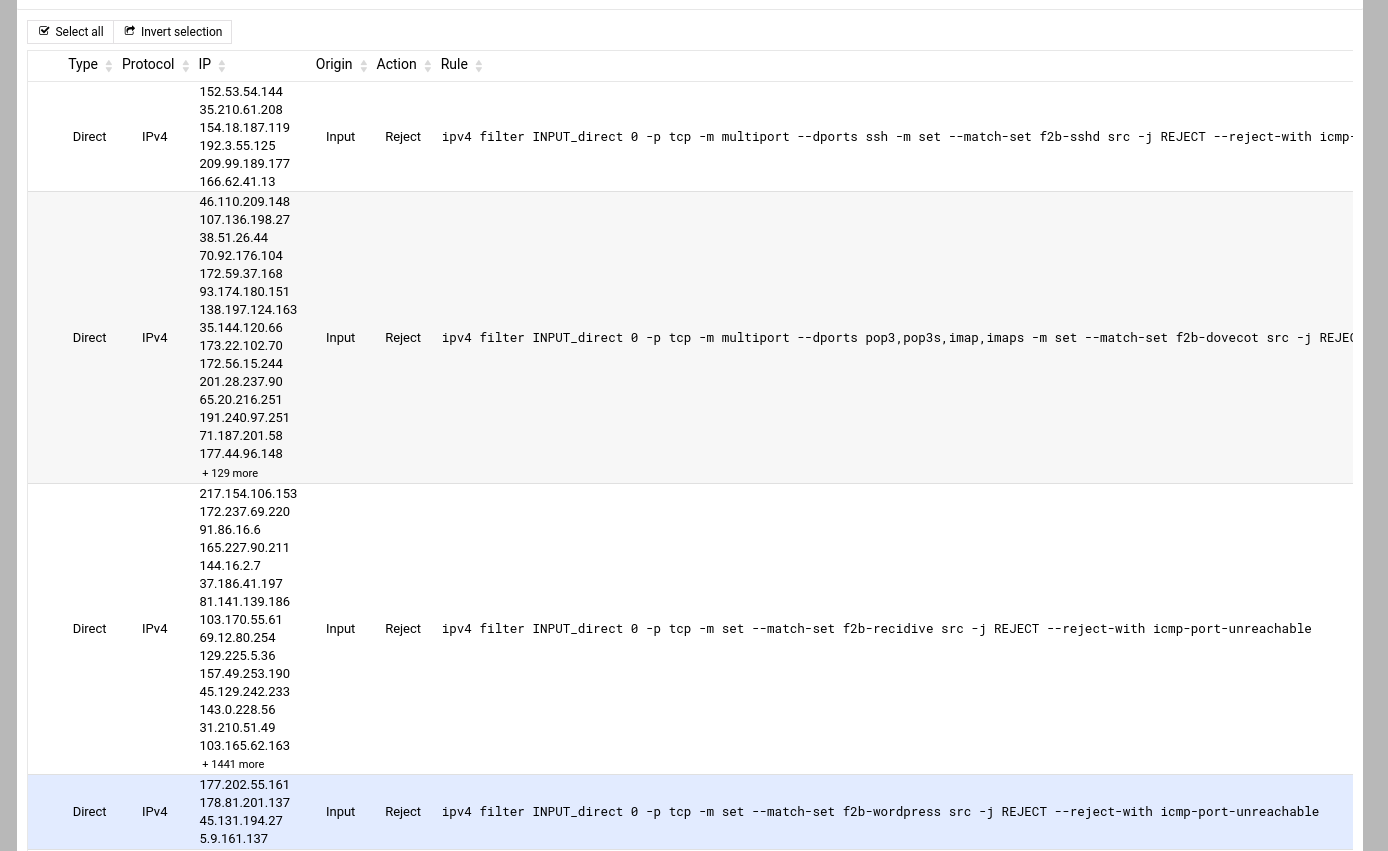
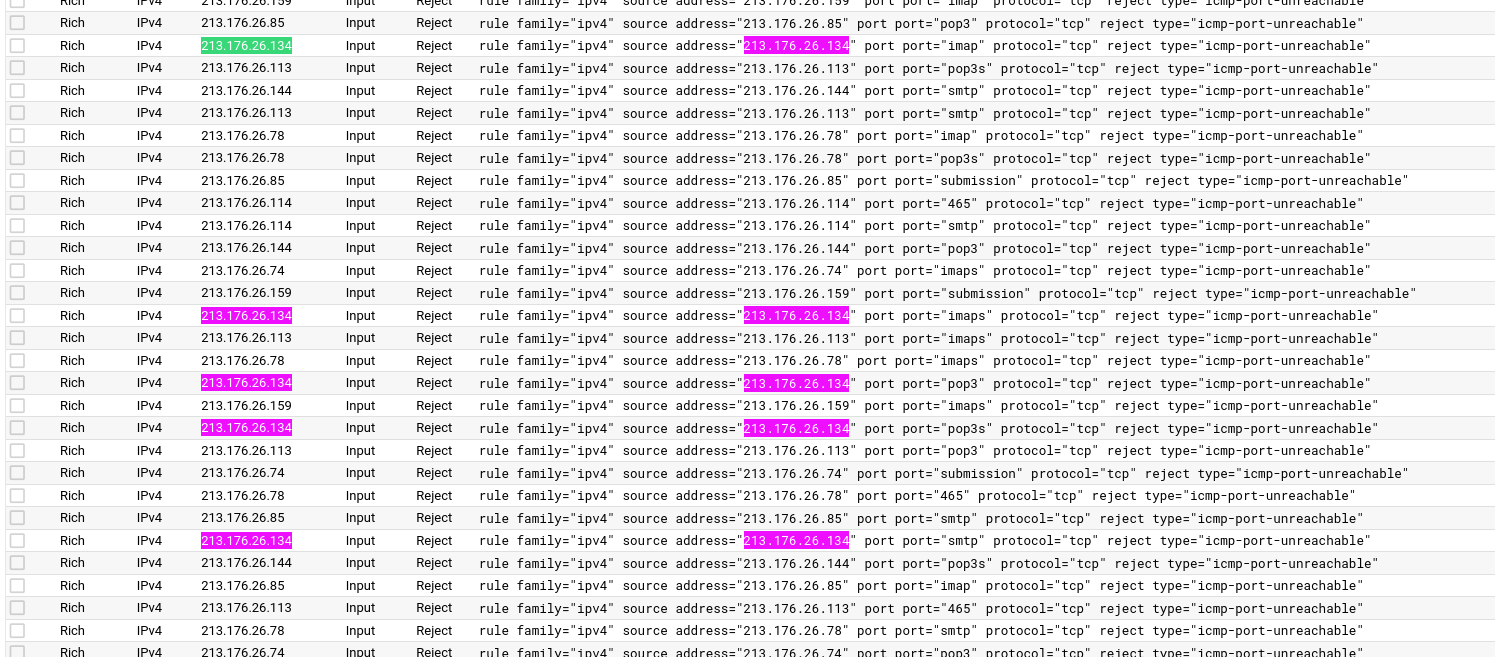
So where we had all ips grouped into the the jail they were put in it now appears we have 1 line per ip address. The interesting is I have noticed is the same IP address is appearing in multiple lines which is telling me the IP address is NOT being banned correctly otherwise this would not be possible
This is leading me to believe something is broken and the rules are not working. For example once an IP is listed in the recidive jail which bans them for a week its should not be possible then reappear in the postfix jail some hours later.
root@ns2:~# dpkg -l | grep firewalld
ii firewalld 2.3.1-1+deb13u1 all dynamically managed firewall with support for network zones
ii python3-firewall 2.3.1-1+deb13u1 all Python3 bindings for firewalld
Thanks, ran into the same problem on Debian 12. When checking the config I wonder why there are rich rules instead of ipsets. Will ask in another topic